Introduction
As an IT manager, you know the importance of protecting your company's data and information systems from security threats. Vulnerability Management is a proactive approach to mitigating such security threats. This article aims to explore the importance of Vulnerability Management for small and medium-sized businesses and how it can help protect your data and information systems.
Understanding Vulnerabilities
Vulnerabilities refer to weaknesses or flaws in IT devices, systems and network infrastructure that can be exploited by attackers to gain unauthorized access, steal data, or disrupt the system's normal functioning. These vulnerabilities can be caused by errors in software code, misconfigured systems, outdated software, or inadequate security protocols.
Vulnerability Management
Vulnerability Management is the process of identifying, assessing, prioritizing, and mitigating vulnerabilities in your organization's endpoint devices and network infrastructure. The goal of Vulnerability Management is to reduce the risk of security breaches by identifying and patching vulnerabilities before attackers can exploit them. The Vulnerability Management process involves the following steps:
- Identify vulnerabilities: This involves conducting regular scans and assessments of your company's endpoint devices and network infrastructure to identify vulnerabilities.
- Assess vulnerabilities: Once vulnerabilities are identified, they are assessed to determine their potential impact on your company's endpoint devices and network infrastructure.
- Prioritize vulnerabilities: Vulnerabilities are prioritized based on their potential impact on your company's endpoint devices and network infrastructure.
- Mitigate vulnerabilities: Vulnerabilities are mitigated by applying security patches, updating software, or implementing security controls.
Benefits of Vulnerability Management
Implementing Vulnerability Management offers several benefits, including:
- Enhanced Security: Vulnerability Management provides organizations with an effective means of identifying and patching vulnerabilities, which helps to enhance the security of their endpoints and network infrastructure.
- Cost Savings: By identifying and mitigating vulnerabilities, organizations can reduce the risk of security breaches, which can result in significant financial losses.
- Compliance: Compliance with industry and government regulations, such as HIPAA, PCI-DSS, and GDPR, requires organizations to implement Vulnerability Management.
- Improved Productivity: Vulnerability Management can help prevent downtime and disruptions caused by security breaches, thereby improving employee productivity.
Implementing Vulnerability Management
Implementing Vulnerability Management involves the following steps:
- Select an automated Vulnerability Management tool: There is a broad selection of ad hoc Vulnerability Scanning solutions on the market, but they are typucally time consuming to configure, run scans and maintain.
- Conduct regular Vulnerability Scans: Organizations should conduct regular scans of their endpoint devices and network infrastructure to identify vulnerabilities.
- Prioritize vulnerabilities: Vulnerabilities should be prioritized based on their potential impact on your company's endpoint devices and network infrastructure.
- Mitigate vulnerabilities: Vulnerabilities should be addressed through the application of security patches, software updates, or the implementation of security controls.
Common Challenges in Vulnerability Management
While implementing Vulnerability Management can provide numerous benefits, it also poses several challenges, such as:
- False positives: Vulnerability Scanners may generate false positives, which can lead to wasted time and resources in addressing irrelevant or non-existent vulnerabilities.
- Time constraints: Conducting regular scans and addressing vulnerabilities can be time-consuming, and many organizations may face challenges in balancing vulnerability management with other operational priorities.
Conclusion
Vulnerability Management is crucial for organizations looking to secure their endpoints and network infrastructure. By implementing a vulnerability management program, organizations can identify and mitigate vulnerabilities before attackers can exploit them, thereby reducing the risk of security breaches. MSPs can find which clients expose vulnerable systems to the internet with EnterProtect Vulnerability Scanning.
Frequently Asked Questions
What is vulnerability management?
Vulnerability Management is the process of identifying, assessing, prioritizing, and mitigating vulnerabilities in your organization's endpoint devices and network infrastructure.
Why is vulnerability management important for small and medium-sized businesses?
Small and medium-sized businesses are often targeted by cybercriminals because they may have weaker security measures in place. Vulnerability Management can help protect their data and information systems by identifying and mitigating vulnerabilities before attackers can exploit them.
What are the steps involved in the vulnerability management process?
The Vulnerability Management process involves identifying vulnerabilities, assessing vulnerabilities, prioritizing vulnerabilities, and mitigating vulnerabilities by applying security patches, updating software, or implementing security controls.
How can organizations implement vulnerability management?
Organizations can implement Vulnerability Management by selecting an automated Vulnerability Management tool, conducting regular Vulnerability Scans, prioritizing vulnerabilities, and mitigating vulnerabilities by applying security patches, updating software, or implementing security controls.
What are the common challenges in vulnerability management?
Common challenges in Vulnerability Management include false positives generated by Vulnerability Scanners and time constraints in conducting regular scans and addressing vulnerabilities.
How often should organizations conduct vulnerability scans?
Organizations should conduct regular Vulnerability Scans to identify vulnerabilities. The frequency of scans will depend on the organization's risk profile, but monthly or quarterly scans are recommended.
What is the CVSS scoring system used in vulnerability management?
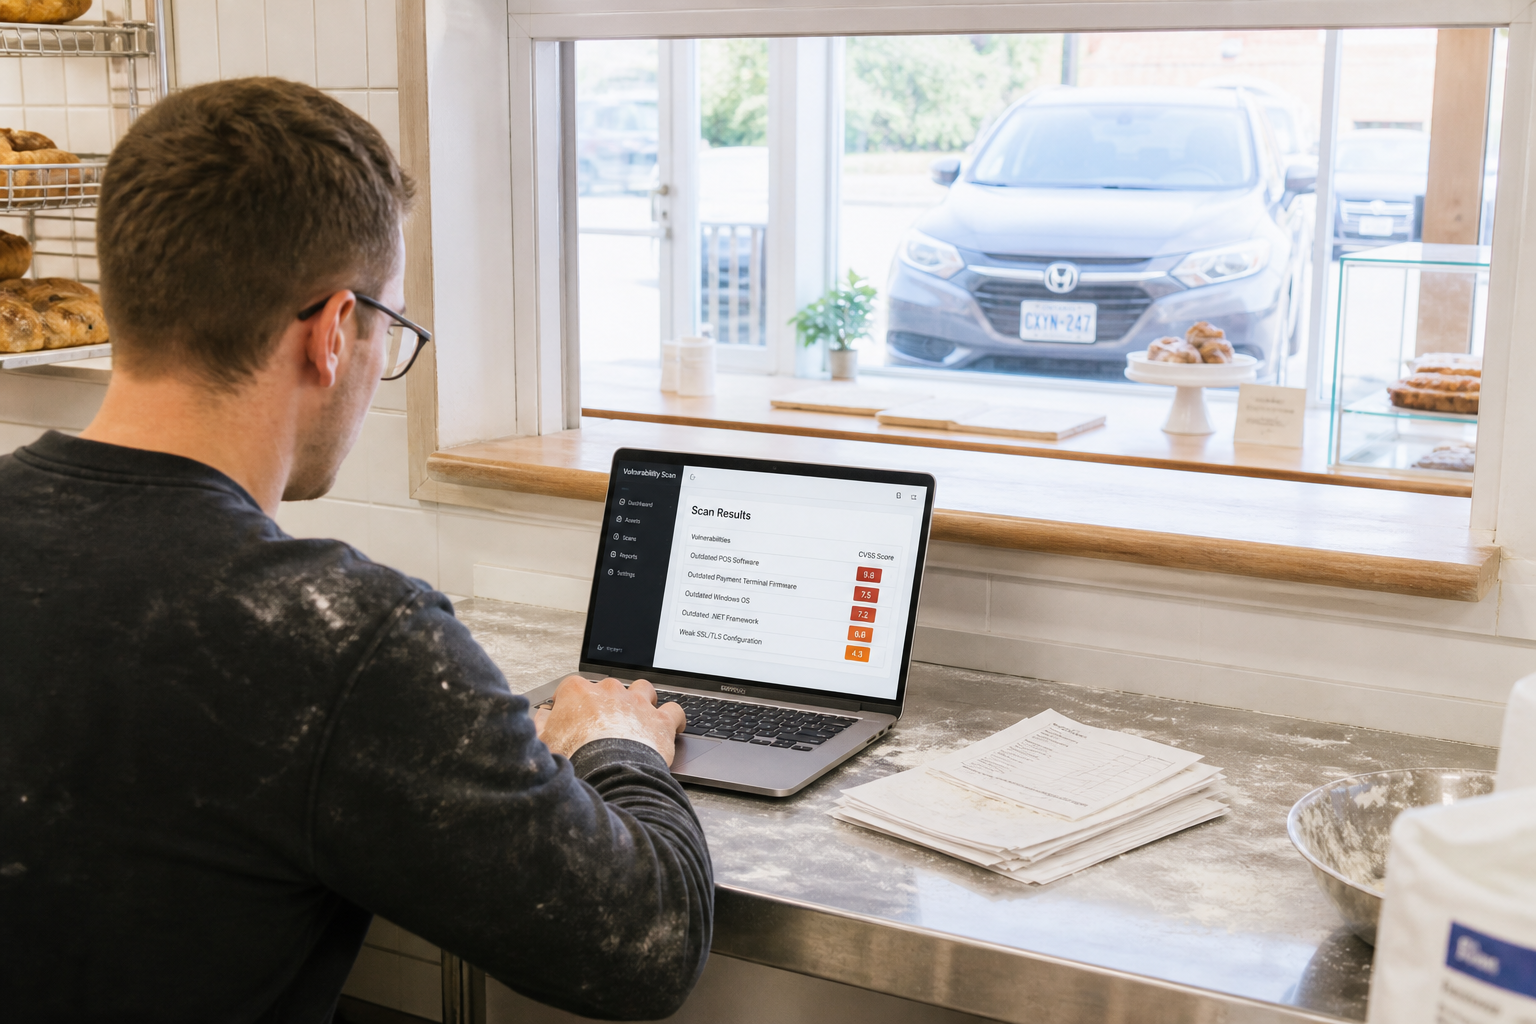
CVSS (Common Vulnerability Scoring System) is a standardized system used to assess the severity of vulnerabilities.
What are the consequences of not implementing vulnerability management?
Not implementing Vulnerability Management can leave an organization's endpoints and network infrastructure vulnerable to attacks, which can result in data breaches, financial losses, and damage to the organization's reputation.