As more and more companies transition to remote workforces, the need for effective cybersecurity measures has never been greater. One critical aspect of securing a remote workforce is monitoring event logs, which can help detect cyber threats before they become serious security breaches. However, remote workforces also present unique challenges to event log monitoring, such as the need to monitor multiple devices and networks outside of a traditional office environment. In this article, we'll explore how event log monitoring can be used to secure remote workforces and provide best practices for implementing this critical security measure.
Types of Cyber Threats to Remote Workforces
As remote workforces continue to expand, cybercriminals are increasingly targeting them with various types of attacks. Here are some of the most common types of cyber threats to remote workforces:
Phishing attacks
Phishing attacks are one of the most common types of cyber attacks. These attacks typically involve sending an email that appears to be from a legitimate source, such as a bank or a company, in an attempt to trick the recipient into providing sensitive information or clicking on a malicious link. With remote workforces, phishing attacks have become more common due to the lack of in-person communication and the increased use of email.
Ransomware attacks
Ransomware attacks involve infecting a computer or network with malware that encrypts files and demands payment in exchange for the decryption key. These attacks can be devastating for remote workers who may not have access to critical files and data.
Insider threats
Insider threats refer to threats posed by employees or contractors who have access to company systems and data. With remote workforces, insider threats can be more difficult to detect and prevent, as employees may be using personal devices or accessing company data from unsecured networks.
Unsecured remote access
Unsecured remote access refers to the use of unsecured remote access tools, such as Remote Desktop Protocol (RDP), which can be exploited by cybercriminals to gain access to a company's network. With remote workforces, the use of unsecured remote access tools can increase the risk of a cyber attack.
How Event Log Monitoring Can Help Mitigate Cyber Risks for Remote Workforces
In today's remote work environment, cybersecurity is more important than ever before. Remote workers are particularly vulnerable to cyber threats due to the use of personal devices, public Wi-Fi networks, and a lack of direct oversight. To combat these threats, event log monitoring is an essential tool for detecting and responding to cyber incidents in real-time.
Event log monitoring is a process of collecting, analyzing, and monitoring log files generated by various systems and applications to detect suspicious activities and potential threats. By analyzing event logs, IT teams can identify and investigate security incidents before they become major issues.
Real-time Threat Detection
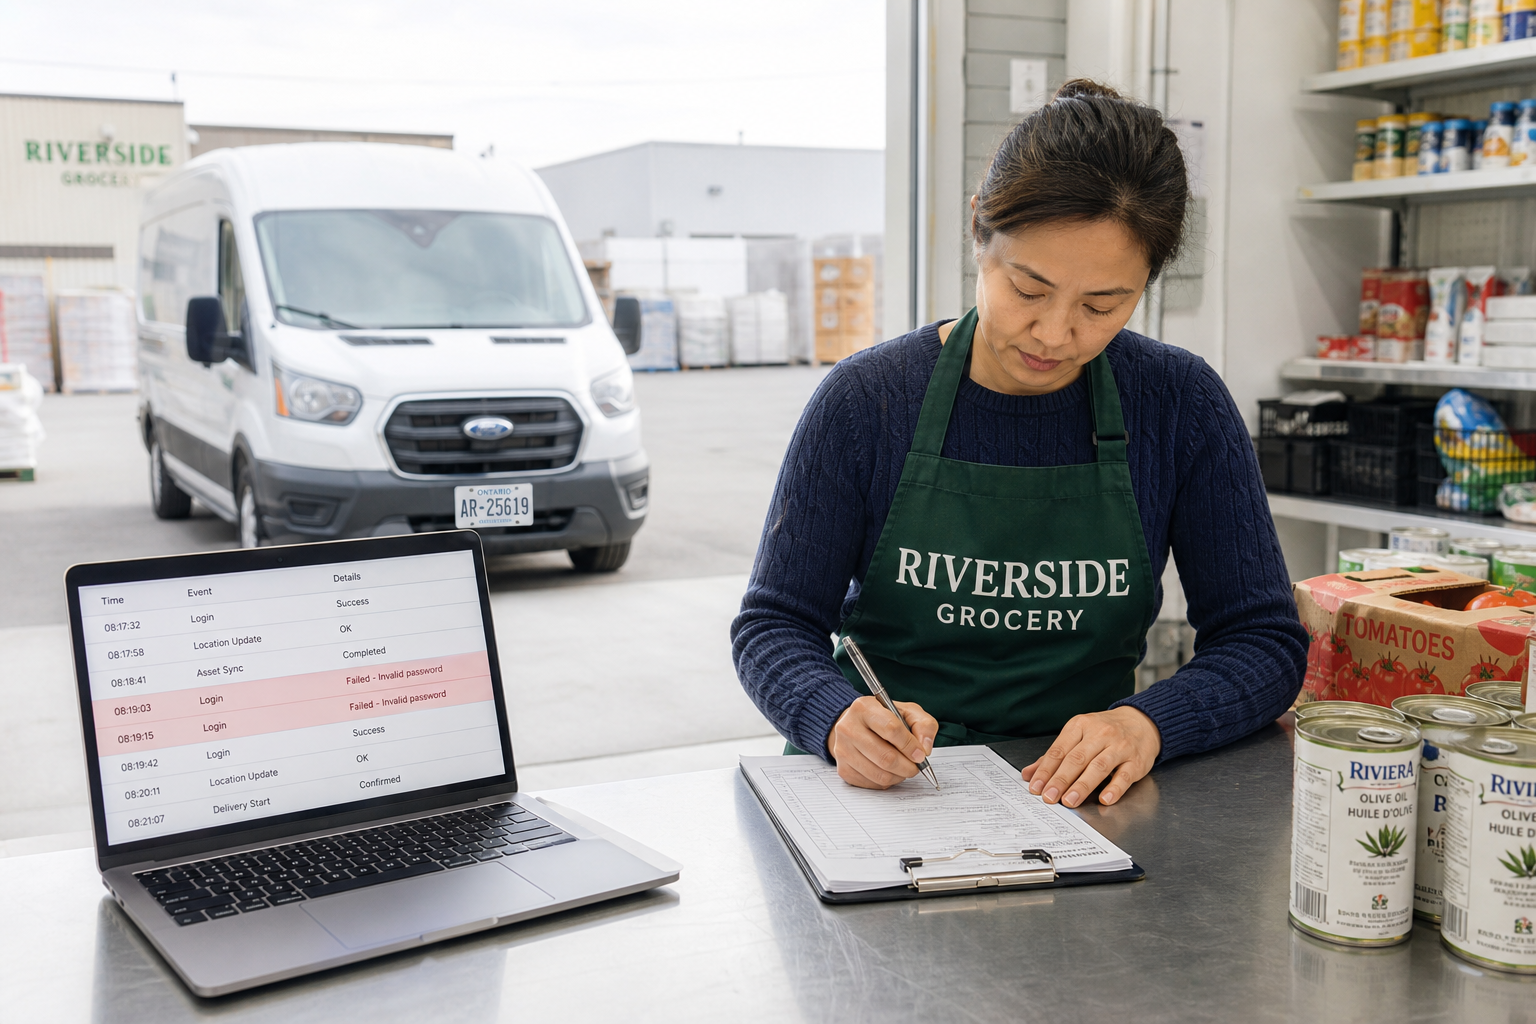
Event log monitoring allows security teams to detect security incidents and potential threats in real-time. By analyzing event logs in real-time, security teams can quickly identify suspicious activities, such as failed login attempts, malware infections, or unauthorized access attempts. This can help security teams take proactive measures to prevent cyber attacks and minimize the impact of security incidents.
Early Warning Signs of Potential Attacks
Event log monitoring can also provide early warning signs of potential cyber attacks. By monitoring event logs for specific events or patterns, security teams can identify activities that could indicate a security incident, such as a data breach or a ransomware attack. This can help security teams take preventive measures to stop the attack before it causes significant damage.
Incident Response and Forensic Investigation
Event log monitoring can also support incident response and forensic investigation activities. By collecting and analyzing event log data, security teams can reconstruct the sequence of events that led to a security incident and identify the root cause of the incident. This can help security teams develop remediation strategies to prevent similar incidents in the future.
Manual Event Log Monitoring for Remote Workforces
Manual event log monitoring involves an IT team member regularly reviewing event logs for signs of suspicious activity. This process can be time-consuming and tedious, but it can be effective if done correctly.
Pros of manual monitoring include the ability to tailor monitoring to the organization's specific needs and greater control over the monitoring process. Cons include the potential for human error and the time and resources required for effective monitoring.
To ensure the effectiveness of manual monitoring, IT teams should establish clear policies and procedures for reviewing event logs, including defining what should be monitored, how often logs should be reviewed, and who will be responsible for reviewing logs. It is also essential to train IT staff on best practices for monitoring and identifying suspicious activity. Additionally, IT teams should have a clear plan in place for responding to any potential threats or incidents identified through event log monitoring.
Automated Event Log Monitoring for Remote Workforces
Automated event log monitoring has become the go-to method for identifying and mitigating cyber risks for remote workforces. This approach involves the use of software tools that automatically collect and analyze event logs generated by remote worker devices, applications, and networks. By analyzing these logs in real-time, automated event log monitoring can identify anomalous behavior that could be indicative of a potential cyber attack or breach.
One major advantage of automated event log monitoring is that it can reduce the time and resources required for manual monitoring. With the use of automated tools, IT teams can monitor a larger number of endpoints and devices with minimal effort. Automated event log monitoring can also provide more accurate and consistent monitoring than manual monitoring, reducing the risk of human error.
Another benefit of automated event log monitoring is that it can provide a more holistic view of an organization's security posture. By monitoring a wide range of event logs, from user logins to network traffic, automated event log monitoring can detect threats that may not be immediately apparent using manual monitoring methods.
However, it is important to note that automated event log monitoring is not a silver bullet solution. IT teams still need to configure and fine-tune the monitoring tools to ensure they are accurately detecting potential threats. Additionally, automated event log monitoring tools may not catch all types of attacks, particularly those that involve sophisticated or novel attack methods.
Overall, automated event log monitoring is a powerful tool that can greatly enhance the security of remote workforces. By providing real-time threat detection and more comprehensive monitoring, IT teams can better protect their organizations from cyber attacks and data breaches.
Conclusion
Event log monitoring is a critical component of cybersecurity. As remote work becomes more prevalent, the risks associated with cyber threats have also increased. By implementing event log monitoring, organizations can quickly detect and respond to potential attacks, reducing the risk of data breaches and other security incidents. Manual event log monitoring can be effective, but it can also be time-consuming and labor-intensive. Regardless of the method used, event log monitoring should be an essential component of any organization's cybersecurity strategy to ensure the safety and security of remote workforces.
Frequently Asked Questions
What is event log monitoring and how does it work?
Event log monitoring involves the continuous tracking and analysis of system event logs to identify security incidents or anomalies. The process involves collecting log data, correlating events, and applying algorithms to detect and alert on suspicious activity.
Can event log monitoring help detect insider threats to remote workforces?
Yes, event log monitoring can help detect insider threats by monitoring user activity and detecting unusual behavior or activity that deviates from established patterns.
How does event log monitoring help with early detection and response to cyber threats for remote workforces?
Event log monitoring provides real-time alerts on potential security incidents, enabling IT teams to respond quickly and prevent further damage. It also allows for the collection of forensic data to investigate incidents and improve future incident response.
What is the difference between manual and automated event log monitoring for remote workforces?
Manual event log monitoring involves the manual review and analysis of logs, which can be time-consuming and prone to human error. Automated event log monitoring, on the other hand, involves the use of software tools to continuously monitor logs and alert on suspicious activity.
What are the best practices for event log monitoring for remote workforces?
Best practices include ensuring log collection is enabled on all remote devices, monitoring for anomalous behavior or activity, implementing multi-factor authentication, and regularly reviewing and updating security policies.
How can event log monitoring help with the security of remote access to corporate networks?
Event log monitoring can help detect unauthorized remote access attempts and prevent data exfiltration. It can also monitor for potential vulnerabilities in remote access tools and alert IT teams to take corrective action.
Can event log monitoring help detect phishing attacks against remote workers?
Yes, event log monitoring can help detect phishing attacks by monitoring email activity and detecting suspicious or malicious emails that may contain phishing links or attachments.
Can event log monitoring be used to monitor cloud-based services used by remote workers?
Yes, event log monitoring can be used to monitor cloud-based services used by remote workers. Logs from cloud services can be collected and analyzed for potential security incidents, such as unauthorized access or data exfiltration.