In today's ever-changing cybersecurity landscape, it's more important than ever to have reliable and effective Endpoint Detection & Response solution. In the 2022 MITRE Engenuity ATT&CK Evaluation, SentinelOne emerged as a clear leader in efficacy, outperforming all competitors with a near perfect score across all tested attack scenarios. In this article, we'll take a closer look at the MITRE Engenuity ATT&CK Evaluation and how SentinelOne performed, as well as what this means for our clients.
100%
Protection & Detection*
Highest
Visibility and Analytic Coverage*
100%
Real-Time. Zero Detection Delays*
* Source: 2022 MITRE Engenuity™ ATT&CK® Evaluation
What Is the MITRE Engenuity ATT&CK Evaluation?
The MITRE Engenuity ATT&CK Evaluation is a third-party analysis of endpoint protection products' efficacy and security. It aims to provide a standardized framework for evaluating how well security solutions perform against different advanced cyberattack scenarios. The evaluation focuses on the MITRE ATT&CK Framework, a globally recognized knowledge base of adversary tactics, techniques, and procedures (TTPs). The evaluation tests each security solution's ability to detect, prevent, and respond to a variety of attacks, from initial access to exfiltration.
The 2022 Enterprise ATT&CK Evaluation emulated the real attack methods of two prominent threat groups: Wizard Spider and Sandworm. These groups are known for their ransomware campaigns, which are aimed at financial gain and data destruction. The evaluation tests the endpoint protection products' ability to defend against the specific tactics, techniques, and procedures used by these groups.
How Did SentinelOne Perform in the 2022 MITRE Engenuity ATT&CK Evaluation?
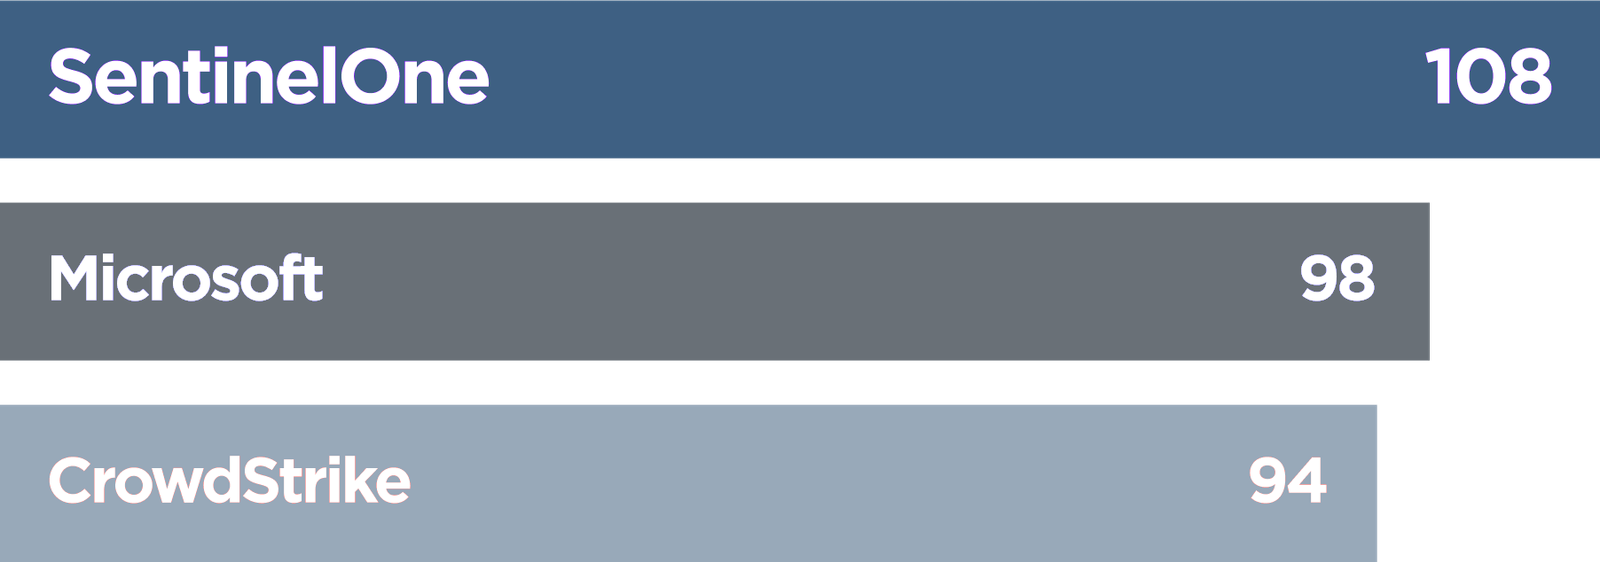
SentinelOne emerged as the leader in efficacy in the 2022 MITRE Engenuity ATT&CK Evaluation. The solution achieved a perfect score across all nine tested MITRE ATT&CK scenarios, with 100% protection and 100% detection of all 19 attack steps. In addition, SentinelOne delivered 100% real-time protection with zero delays, meaning that all detections occurred in real-time, without the need for manual investigation. SentinelOne also delivered the highest visibility and analytic coverage across all tested operating systems (Windows and Linux) for the third year in a row.
Analytic detections
Highest Analytic Coverage: 108 of 109 Detections
Analytic detections provide contextualized data that helps uncover the attacker’s intention and the techniques they used. SentinelOne delivered the highest analytic coverage across all tested operating systems—Windows and Linux®—for the third year in a row.
| Coverage | |
|---|---|
| SentinelOne | 99 |
| Cyberreason | 99 |
| BitDefender | 97 |
| TrendMicro | 92 |
| Microsoft | 90 |
| Crowdstrike | 86 |
| FireEye | 78 |
| McAfee | 77 |
| MalwareBytes | 76 |
| Symantec | 72 |
| Cisco | 68 |
| Cylance | 65 |
| ESET | 63 |
| Sophos | 61 |
| Carbon Black | 52 |
Delays
100% Real-Time Protection: 0 Delays
Delayed detections require security analysts to manually investigate activity. SentinelOne detection happens in real time, meaning zero delayed detections.
| Delays | |
|---|---|
| SentinelOne | 0 |
| FireEye | 1 |
| Sophos | 2 |
| Symantec | 5 |
| Cisco | 7 |
| CrowdStrike | 11 |
EDR is an upgrade to traditional antivirus (AV) solutions that offer greater visibility, detection, and response capabilities.
What is EDR?
Endpoint Detection & Response (EDR) is a security technology that monitors endpoints and provides real-time visibility into security incidents. It enables security teams to quickly detect, investigate, and respond to threats, reducing the dwell time of attackers in the network.
AI-Based Ransomware Protection
EDR solutions like SentinelOne use advanced AI-based algorithms to detect and respond to ransomware attacks. This enables them to detect and stop ransomware attacks before they can cause damage to the network.
Automated Threat Response
EDR solutions automate threat response, allowing IT teams to respond to threats quickly and effectively. This reduces the dwell time of attackers in the network, minimizing the impact of attacks.
Malware/Ransomware Rollback
EDR solutions like SentinelOne offer malware and ransomware rollback, which allows IT teams to roll back infected devices to their pre-infected state. This can be done in a matter of minutes, avoiding costly outages, data loss, and ransom payments.
Threat Intelligence and Indicators
EDR solutions like SentinelOne use threat intelligence and indicators to detect and respond to threats quickly. This allows IT teams to prioritize the most critical threats and respond to them before they can cause damage to the network.
Incident Forensics Reporting
EDR solutions like SentinelOne offer detailed incident forensics reporting, allowing IT teams to investigate incidents and identify the root cause of the attack. This information can be used to improve the overall security posture of the organization.
EDR: an Upgrade to Traditional AV
Traditional AV solutions are designed to detect and block known malware threats. However, they are often unable to detect new and emerging threats. EDR solutions like SentinelOne use advanced behavioral detection algorithms and threat intelligence to detect and respond to new and emerging threats. This helps your organization to defend against evolving threats and respond to threat incidents 3x faster than with traditional AV.
What Does This Mean for You?
SentinelOne's performance in the 2022 MITRE Engenuity ATT&CK Evaluation demonstrates its efficacy and ability to protect against a wide range of cyber threats.
Endpoint Protection is a critical components of any cybersecurity strategy.
Conclusion
The 2022 MITRE Engenuity ATT&CK Evaluation results demonstrate the effectiveness of SentinelOne's Endpoint Detection & Response capabilities. By achieving a near perfect score across all tested attack scenarios, SentinelOne has proven its ability to protect against a wide range of cyber threats.