In today's interconnected business world, supply chain management is critical to the success of organizations. Companies are increasingly relying on a vast network of suppliers, vendors, and partners to provide the goods and services necessary to keep their operations running smoothly. However, this interconnectivity also brings with it the risk of cyber threats that can impact the entire supply chain. One key way to mitigate these risks is through event log monitoring. In this article, we will explore how event log monitoring can help organizations better manage supply chain cyber risks and ensure their operations remain secure.
Types of Supply Chain Cyber Risks
Supply chains are complex systems that often involve multiple third-party vendors, which can increase the risk of cyber threats. Some of the most common types of supply chain cyber risks include:
Malware infection
Malware can be introduced into a supply chain through a number of different methods, including through emails, software downloads, or infected devices. Once malware infects a system, it can be used to steal data, disrupt operations, or cause other types of damage.
Data breaches
Data breaches can occur when sensitive information is stolen or compromised, such as customer data or financial information. A supply chain breach can have far-reaching consequences, affecting multiple organizations along the chain.
Third-party access
Third-party access can pose a risk to supply chains, particularly if vendors have access to sensitive data or systems. If a vendor's system is breached, it can provide a gateway for attackers to access other parts of the supply chain.
Insider threats
Insider threats can come from within an organization, such as an employee who has access to sensitive information. These types of threats can be difficult to detect and prevent.
Counterfeit software or hardware
Counterfeit software or hardware can be introduced into a supply chain through a variety of means, such as by hackers or through unauthorized resellers. This can create security vulnerabilities or cause other types of problems.
Unsecured networks or devices
Unsecured networks or devices can be a weak point in a supply chain, particularly if vendors or partners are using outdated or vulnerable systems. Attackers can exploit these weaknesses to gain access to sensitive information or systems.
How Event Log Monitoring Can Help Mitigate Supply Chain Cyber Risks
One of the most effective ways to mitigate supply chain cyber risks is through event log monitoring. This involves collecting and analyzing event logs from various devices and systems across the supply chain to identify potential threats and vulnerabilities.
Explanation of Event Log Monitoring
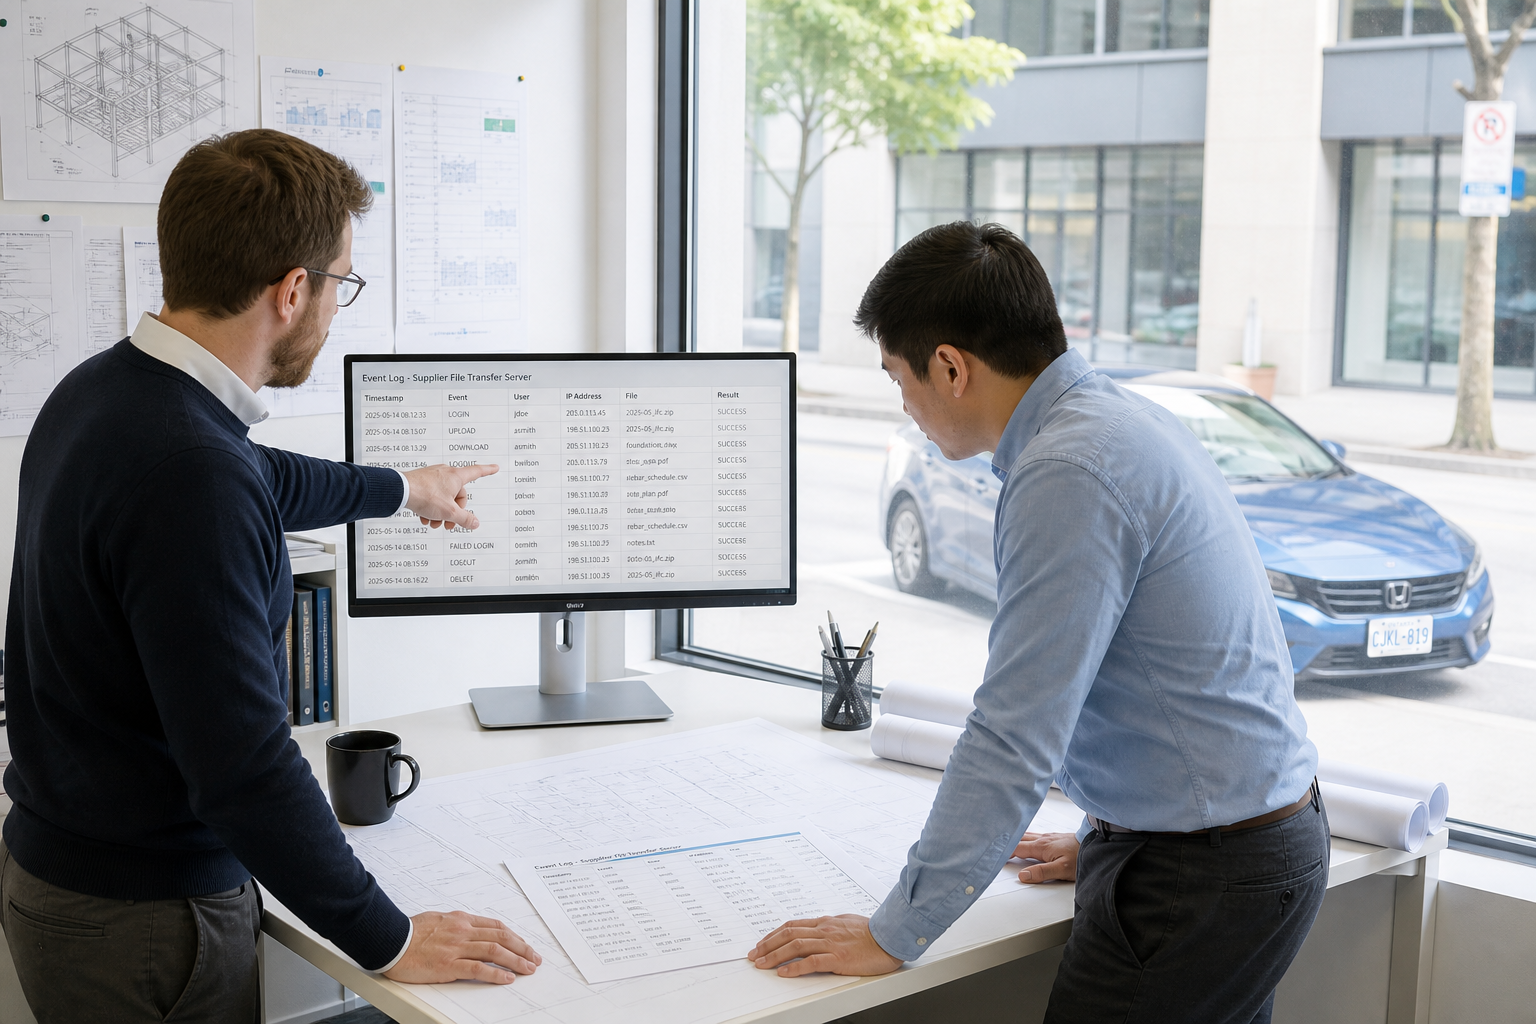
Event log monitoring involves collecting, storing, and analyzing event logs from various sources, including servers, workstations, network devices, and security devices. Event logs are records of activity that occur on a device or system and can include information such as logins, logouts, file access, system events, and network connections.
Real-Time Threat Detection
By monitoring event logs in real-time, IT professionals can detect and respond to potential threats before they become major security incidents. This can include identifying suspicious login attempts, unusual network traffic, or unauthorized access to critical systems or data.
Early Warning Signs of Potential Attacks
Event log monitoring can also provide early warning signs of potential attacks, allowing IT teams to take proactive measures to prevent them. For example, event log monitoring can detect attempts to install malware or ransomware on devices or systems, and can also identify attempts to exfiltrate data from the supply chain.
Incident Response and Forensic Investigation
Finally, event log monitoring can help with incident response and forensic investigation in the event of a security incident. By collecting and analyzing event logs from before, during, and after an incident, IT teams can gain insights into the attack and identify the root cause, as well as take measures to prevent similar incidents from occurring in the future.
Best Practices for Implementing Event Log Monitoring in Supply Chain Management
To effectively use event log monitoring to mitigate supply chain cyber risks, it is important to follow certain best practices. Here are some of the best practices for implementing event log monitoring in supply chain management:
Regularly review and update security policies
Regularly review and update your organization's security policies to ensure that they are up-to-date and comprehensive. Make sure that all suppliers, vendors, and partners are aware of your security policies and comply with them.
Monitor vendor and third-party access
Monitor all vendor and third-party access to your network and systems. This includes monitoring logins, logouts, and any changes made to user permissions. Implement a strong vendor management program to ensure that all third-party vendors are thoroughly vetted before being granted access to your network.
Keep software and hardware up-to-date
Keep all software and hardware up-to-date with the latest security patches and updates. Regularly monitor your systems for vulnerabilities and address any issues as soon as possible.
Regularly train employees on cybersecurity best practices
Regularly train your employees on cybersecurity best practices, such as how to identify and report suspicious activity. Make sure that all employees are aware of the risks associated with supply chain cyber attacks and how to avoid them.
Continuously monitor event logs
Continuously monitor event logs for any suspicious activity or anomalies. Make sure that you have automated tools in place to alert you of any potential threats in real-time. This will help you detect and respond to cyber threats before they can cause significant damage.
Conclusion
As the threat landscape continues to evolve, businesses must implement effective cybersecurity strategies to mitigate the risks to their supply chains. Event log monitoring is a critical component of any comprehensive cybersecurity plan, enabling real-time threat detection, early warning signs of potential attacks, and effective incident response and forensic investigation. With continuous monitoring and proactive measures, businesses can gain greater visibility into their supply chains and stay ahead of potential attacks, safeguarding their data and reputation.
Frequently Asked Questions
What is supply chain cyber risk?
Supply chain cyber risk refers to the potential for cyber attacks to target an organization through vulnerabilities in its supply chain, such as third-party vendors or suppliers.
What are some examples of supply chain cyber risks?
Examples of supply chain cyber risks include malware infection, data breaches, third-party access, insider threats, counterfeit software or hardware, and unsecured networks or devices.
How can event log monitoring help mitigate supply chain cyber risks?
Event log monitoring can help organizations detect and respond to potential supply chain cyber risks in real-time by providing early warning signs of potential attacks and supporting incident response and forensic investigation efforts.
What are some best practices for implementing event log monitoring in supply chain management?
Best practices for implementing event log monitoring in supply chain management include regularly reviewing and updating security policies, monitoring vendor and third-party access, keeping software and hardware up-to-date, regularly training employees on cybersecurity best practices, and continuously monitoring event logs.
How can regular training on cybersecurity best practices help mitigate supply chain cyber risks?
Regular training on cybersecurity best practices can help employees and partners better understand the risks and implications of supply chain cyber attacks and take proactive measures to prevent them.
How can organizations identify vulnerabilities in their supply chain?
Organizations can identify vulnerabilities in their supply chain by conducting regular risk assessments and audits, implementing vendor risk management policies, and establishing a clear supply chain security strategy.
How can organizations balance supply chain efficiency with cybersecurity?
Organizations can balance supply chain efficiency with cybersecurity by incorporating security requirements into vendor and supplier contracts, implementing robust security policies and procedures, and regularly assessing and monitoring supply chain risks.
How does supply chain cyber risk impact small and medium-sized businesses?
Small and medium-sized businesses may be particularly vulnerable to supply chain cyber risks due to limited resources, lack of expertise, and dependence on third-party vendors and suppliers. It is important for these businesses to prioritize supply chain security and implement effective risk management strategies.